Hi, i'm Zaw

A platform engineer driven by building resilient and reliable systems

Singapore

Contact Me
Platform engineering in actionHomelab demos / 2026

About me

Expertise

01

Platform Engineering

Production Kubernetes and OpenShift platforms, from node lifecycle and storage to RBAC, network policy, and reliable Day-2 operations.

02

Site Reliability

Incident response, root-cause analysis, and actionable observability with Prometheus, Grafana, ELK, OpenSearch, and Zabbix.

03

Automation & GitOps

Repeatable infrastructure with Terraform and Ansible. Git-driven delivery with ArgoCD, Jenkins, and automated container pipelines.

04

Security & Hardening

CIS and IM8-aligned controls, vulnerability remediation, policy-as-code, and secure access with Vault, CyberArk, and Entra ID.

05

Software & Data Systems

Real-time IoT dashboards and data pipelines, highly available MariaDB clusters, and web and mobile applications built around real operational needs.

Project

Systems built. Lessons learned. Always evolving.

01

Self-directed / Infrastructure

Homelab Platform

Explore GitHub
Homelab Platform concept artwork, detail oneHomelab Platform concept artwork, detail two
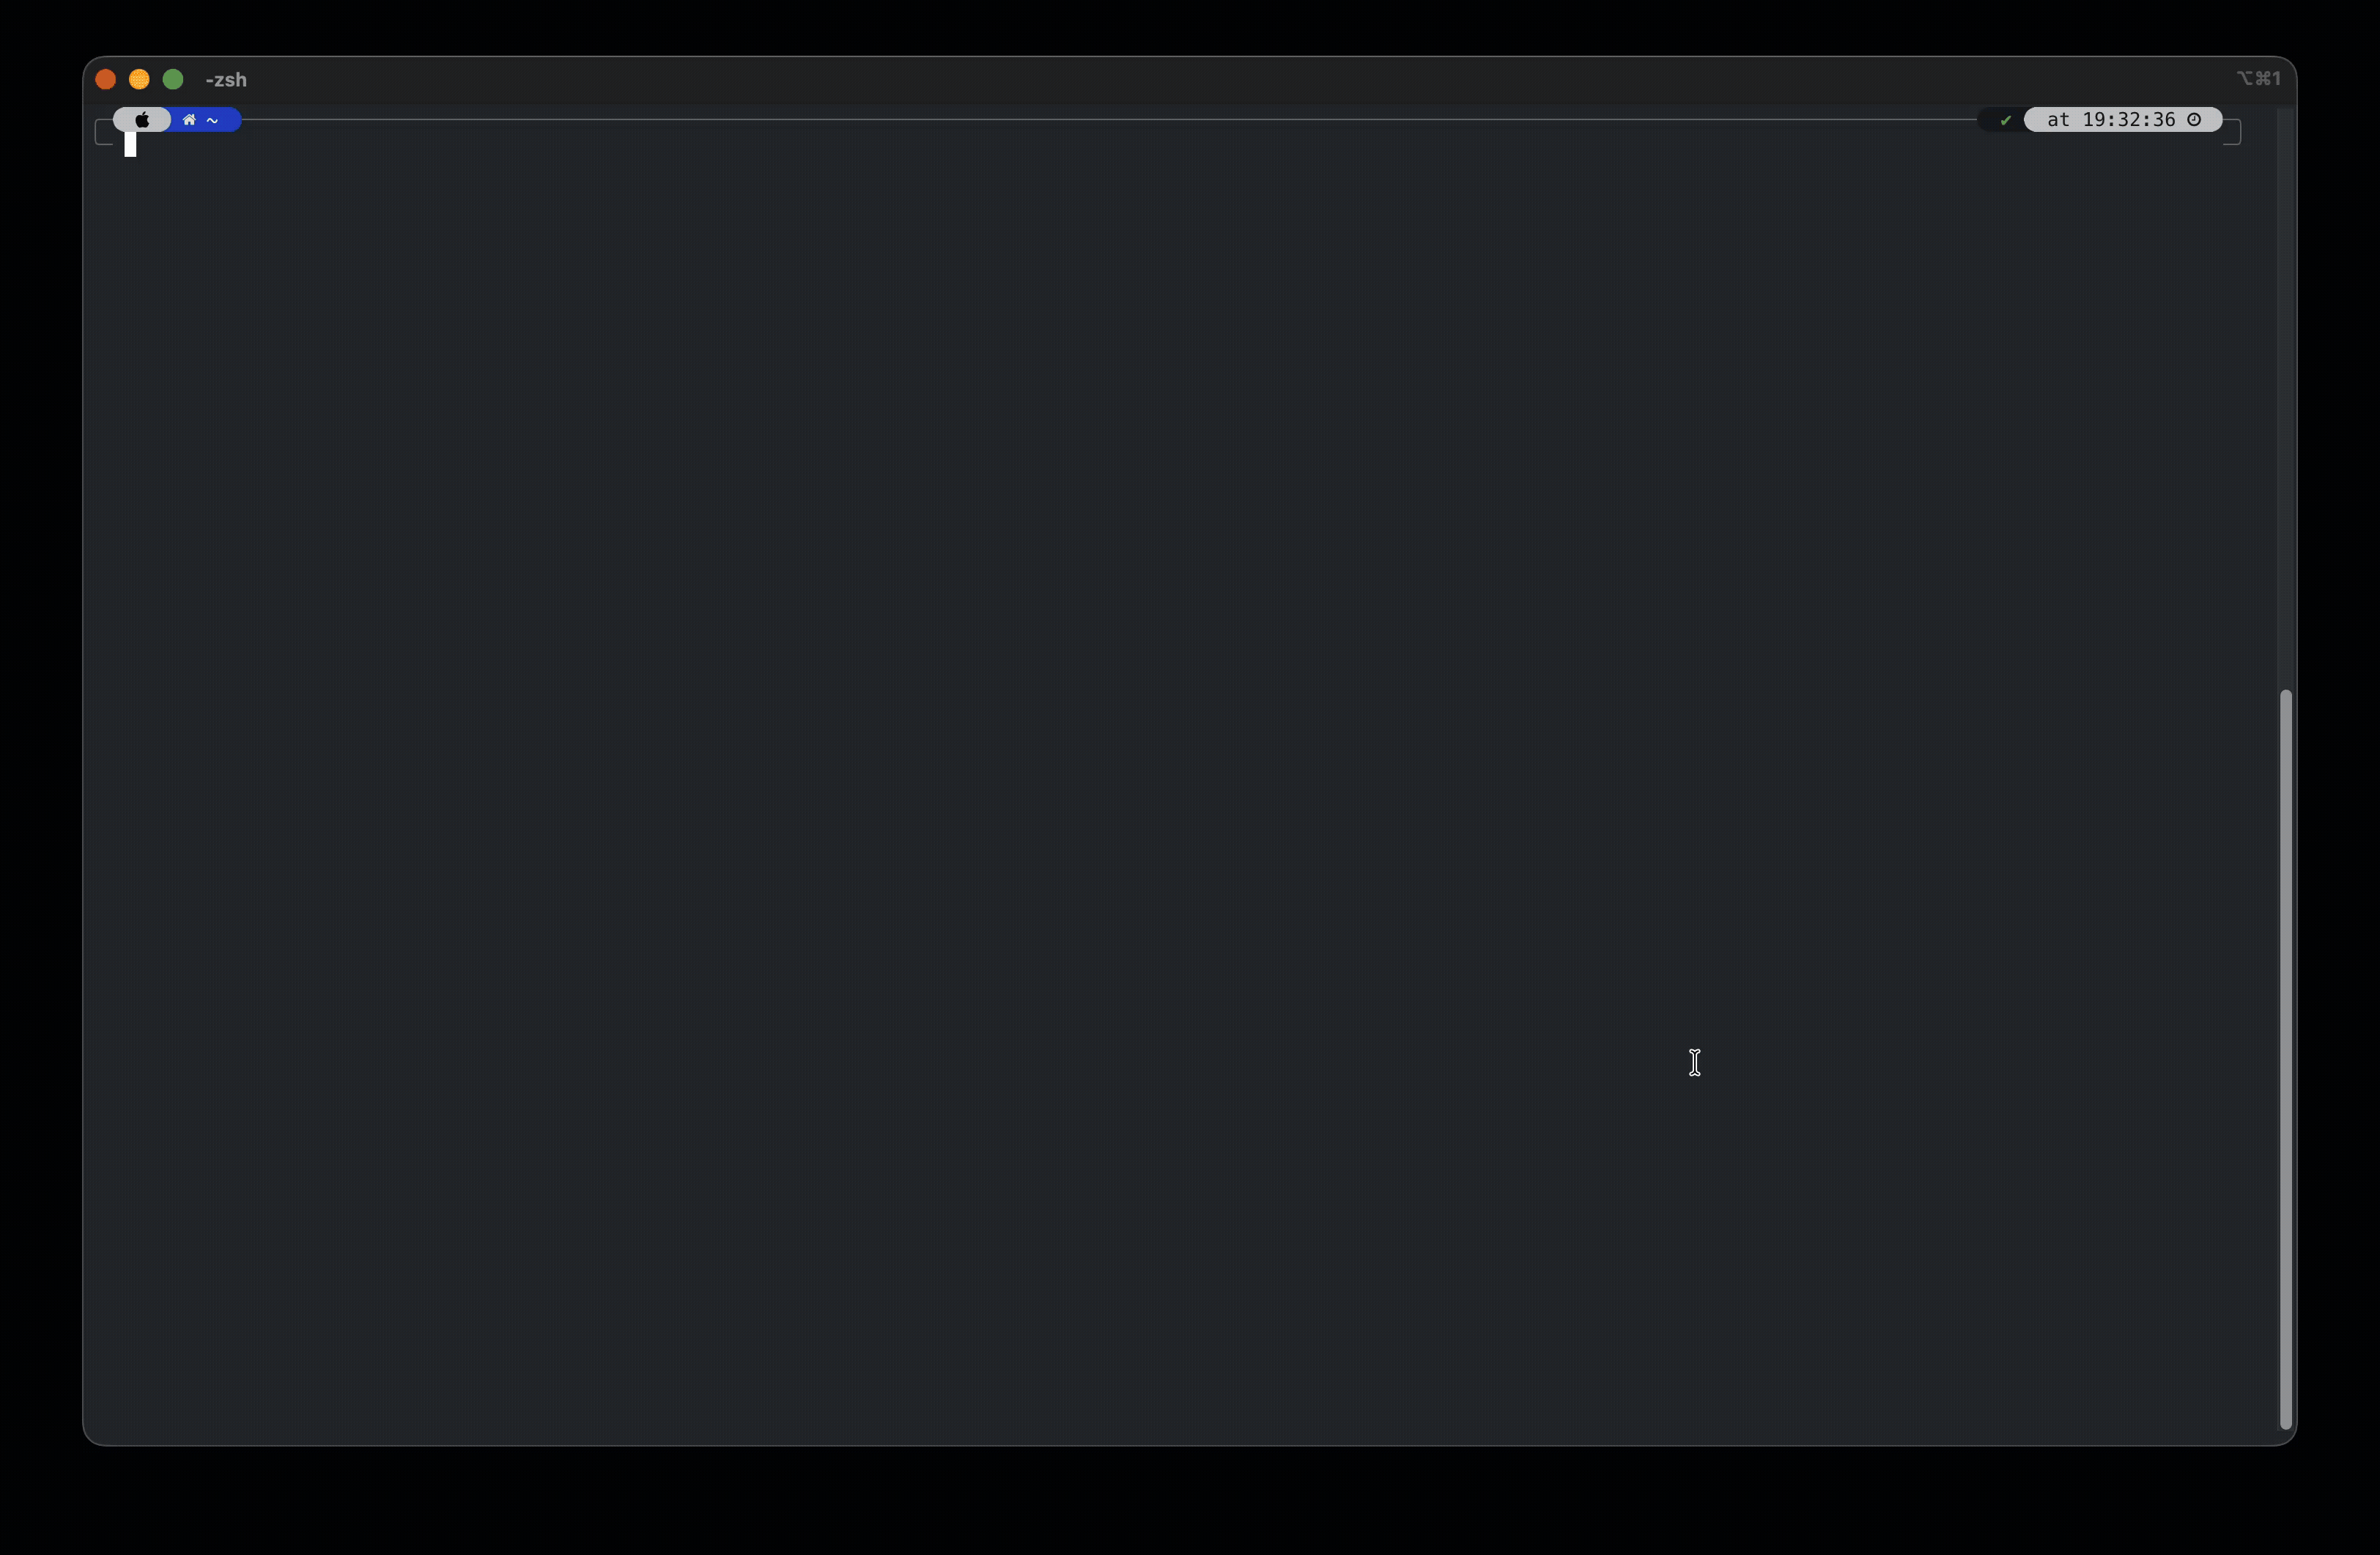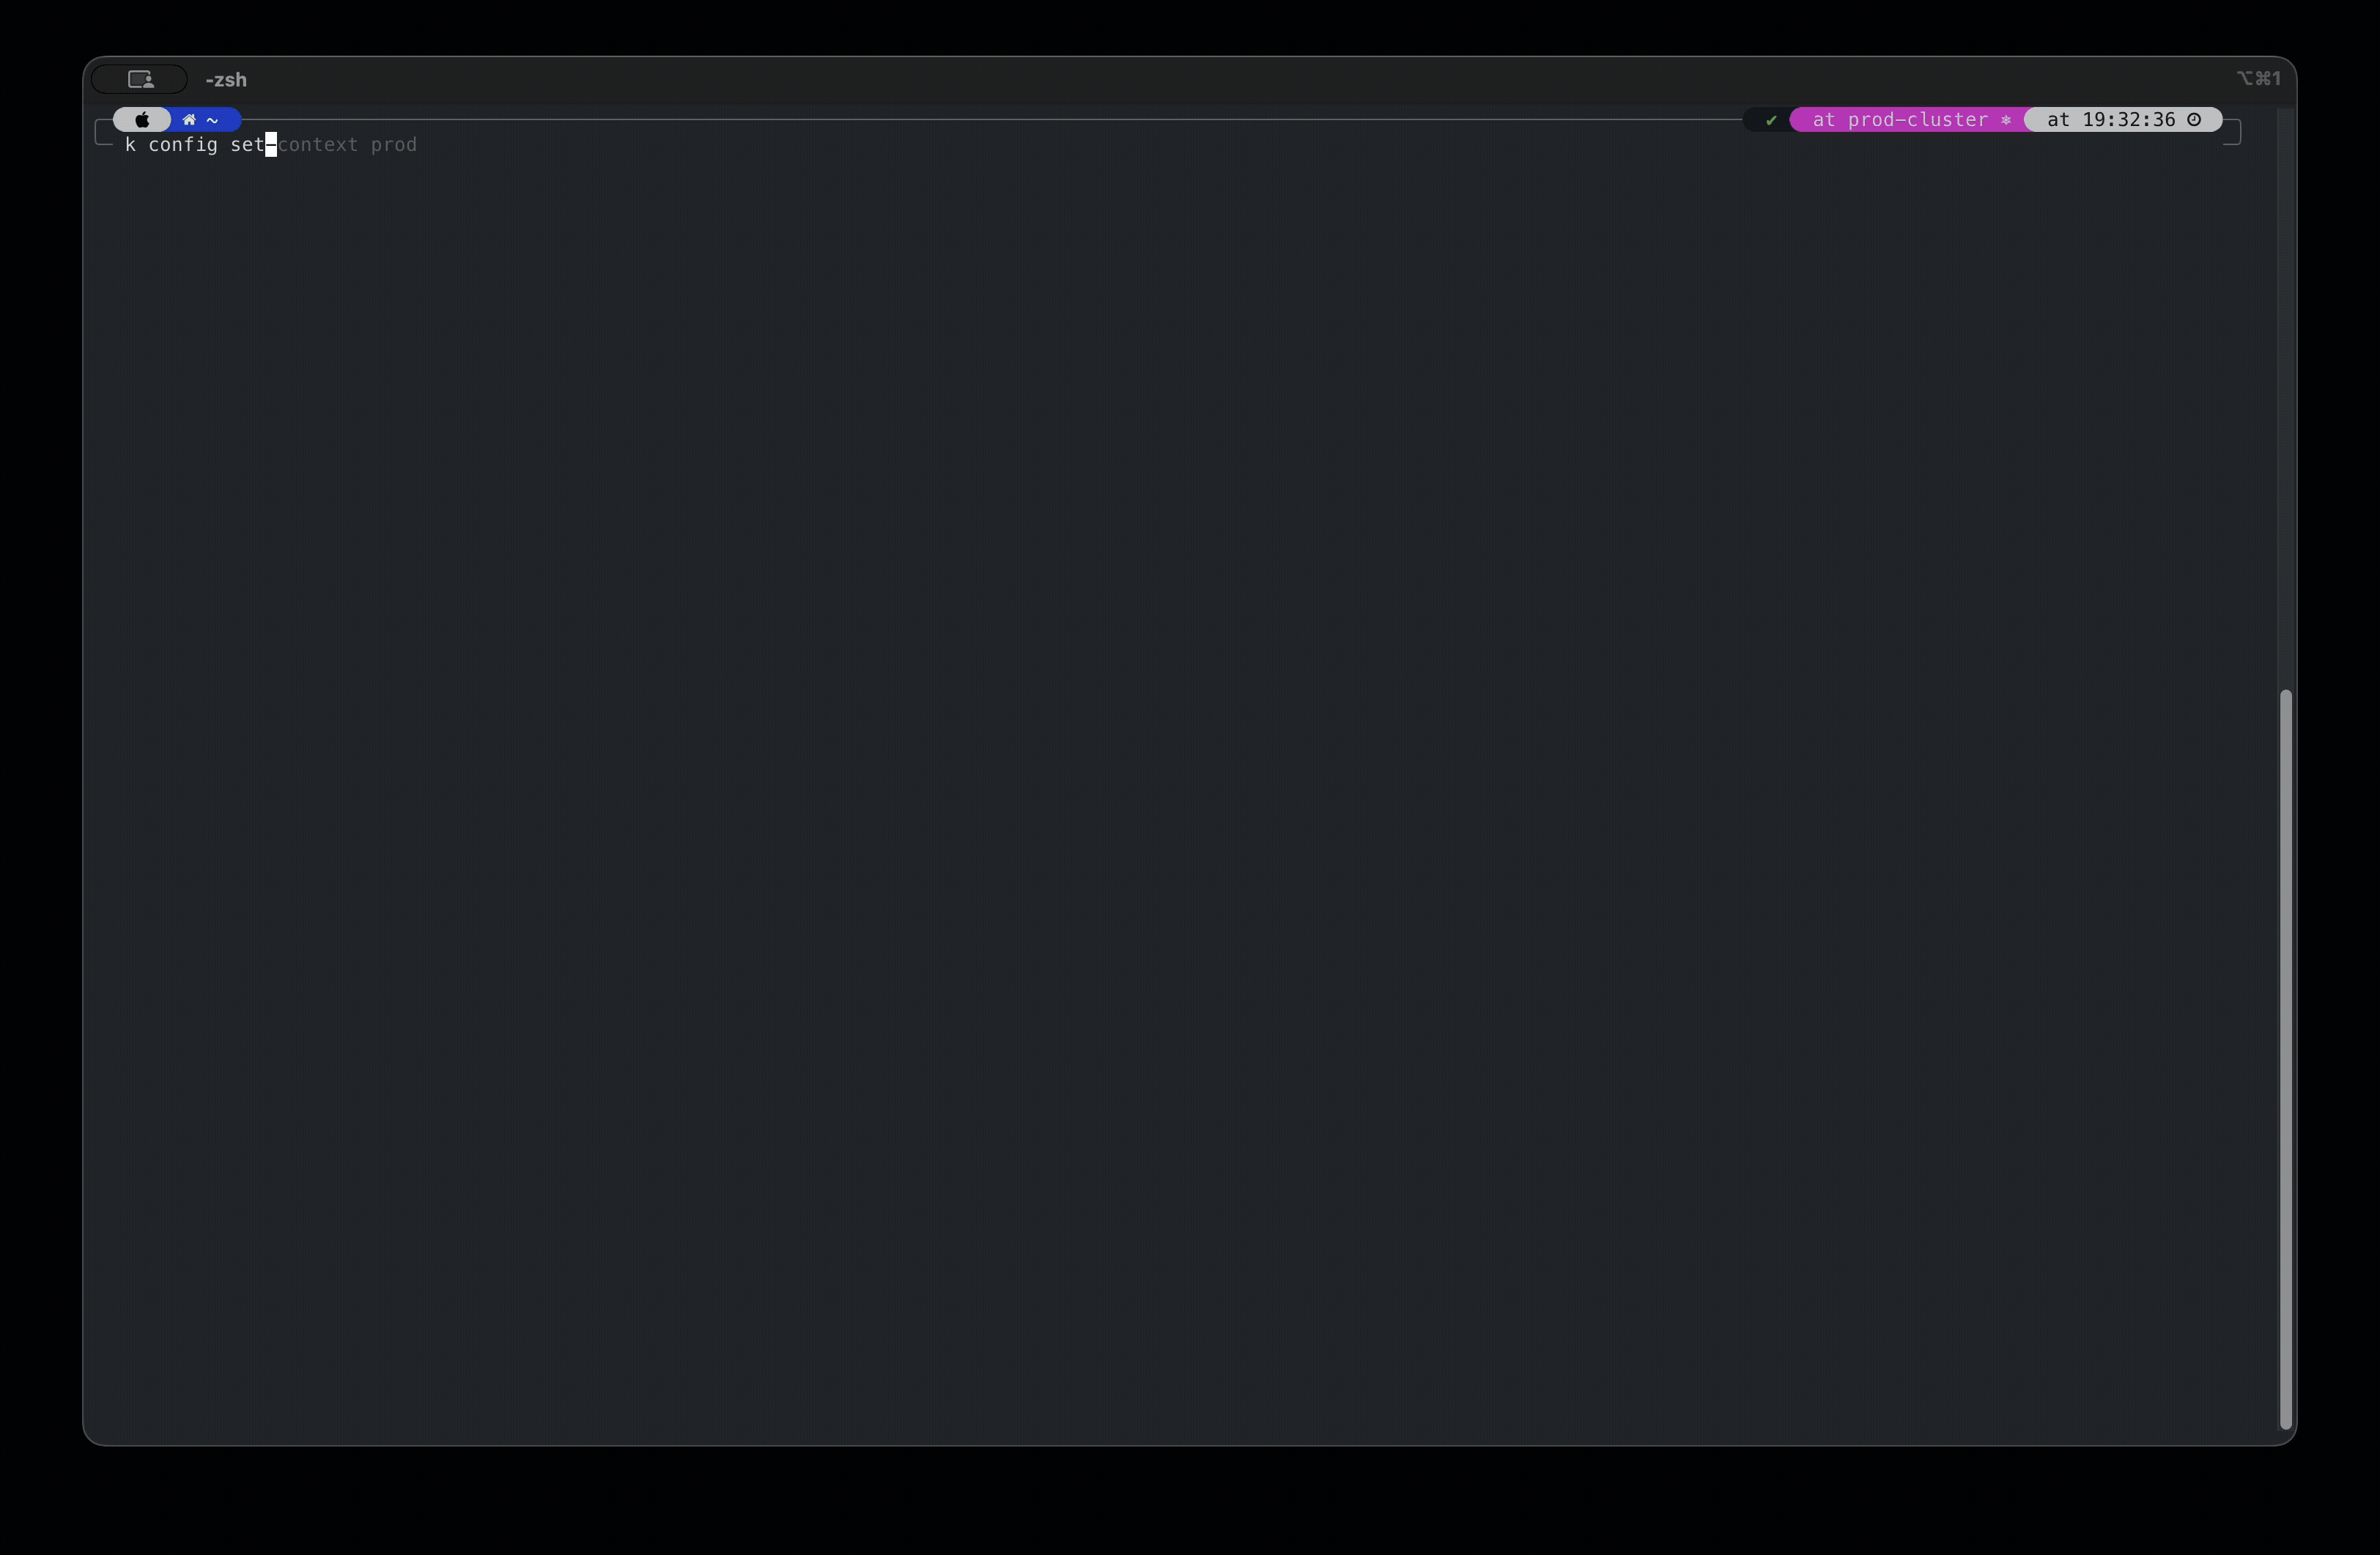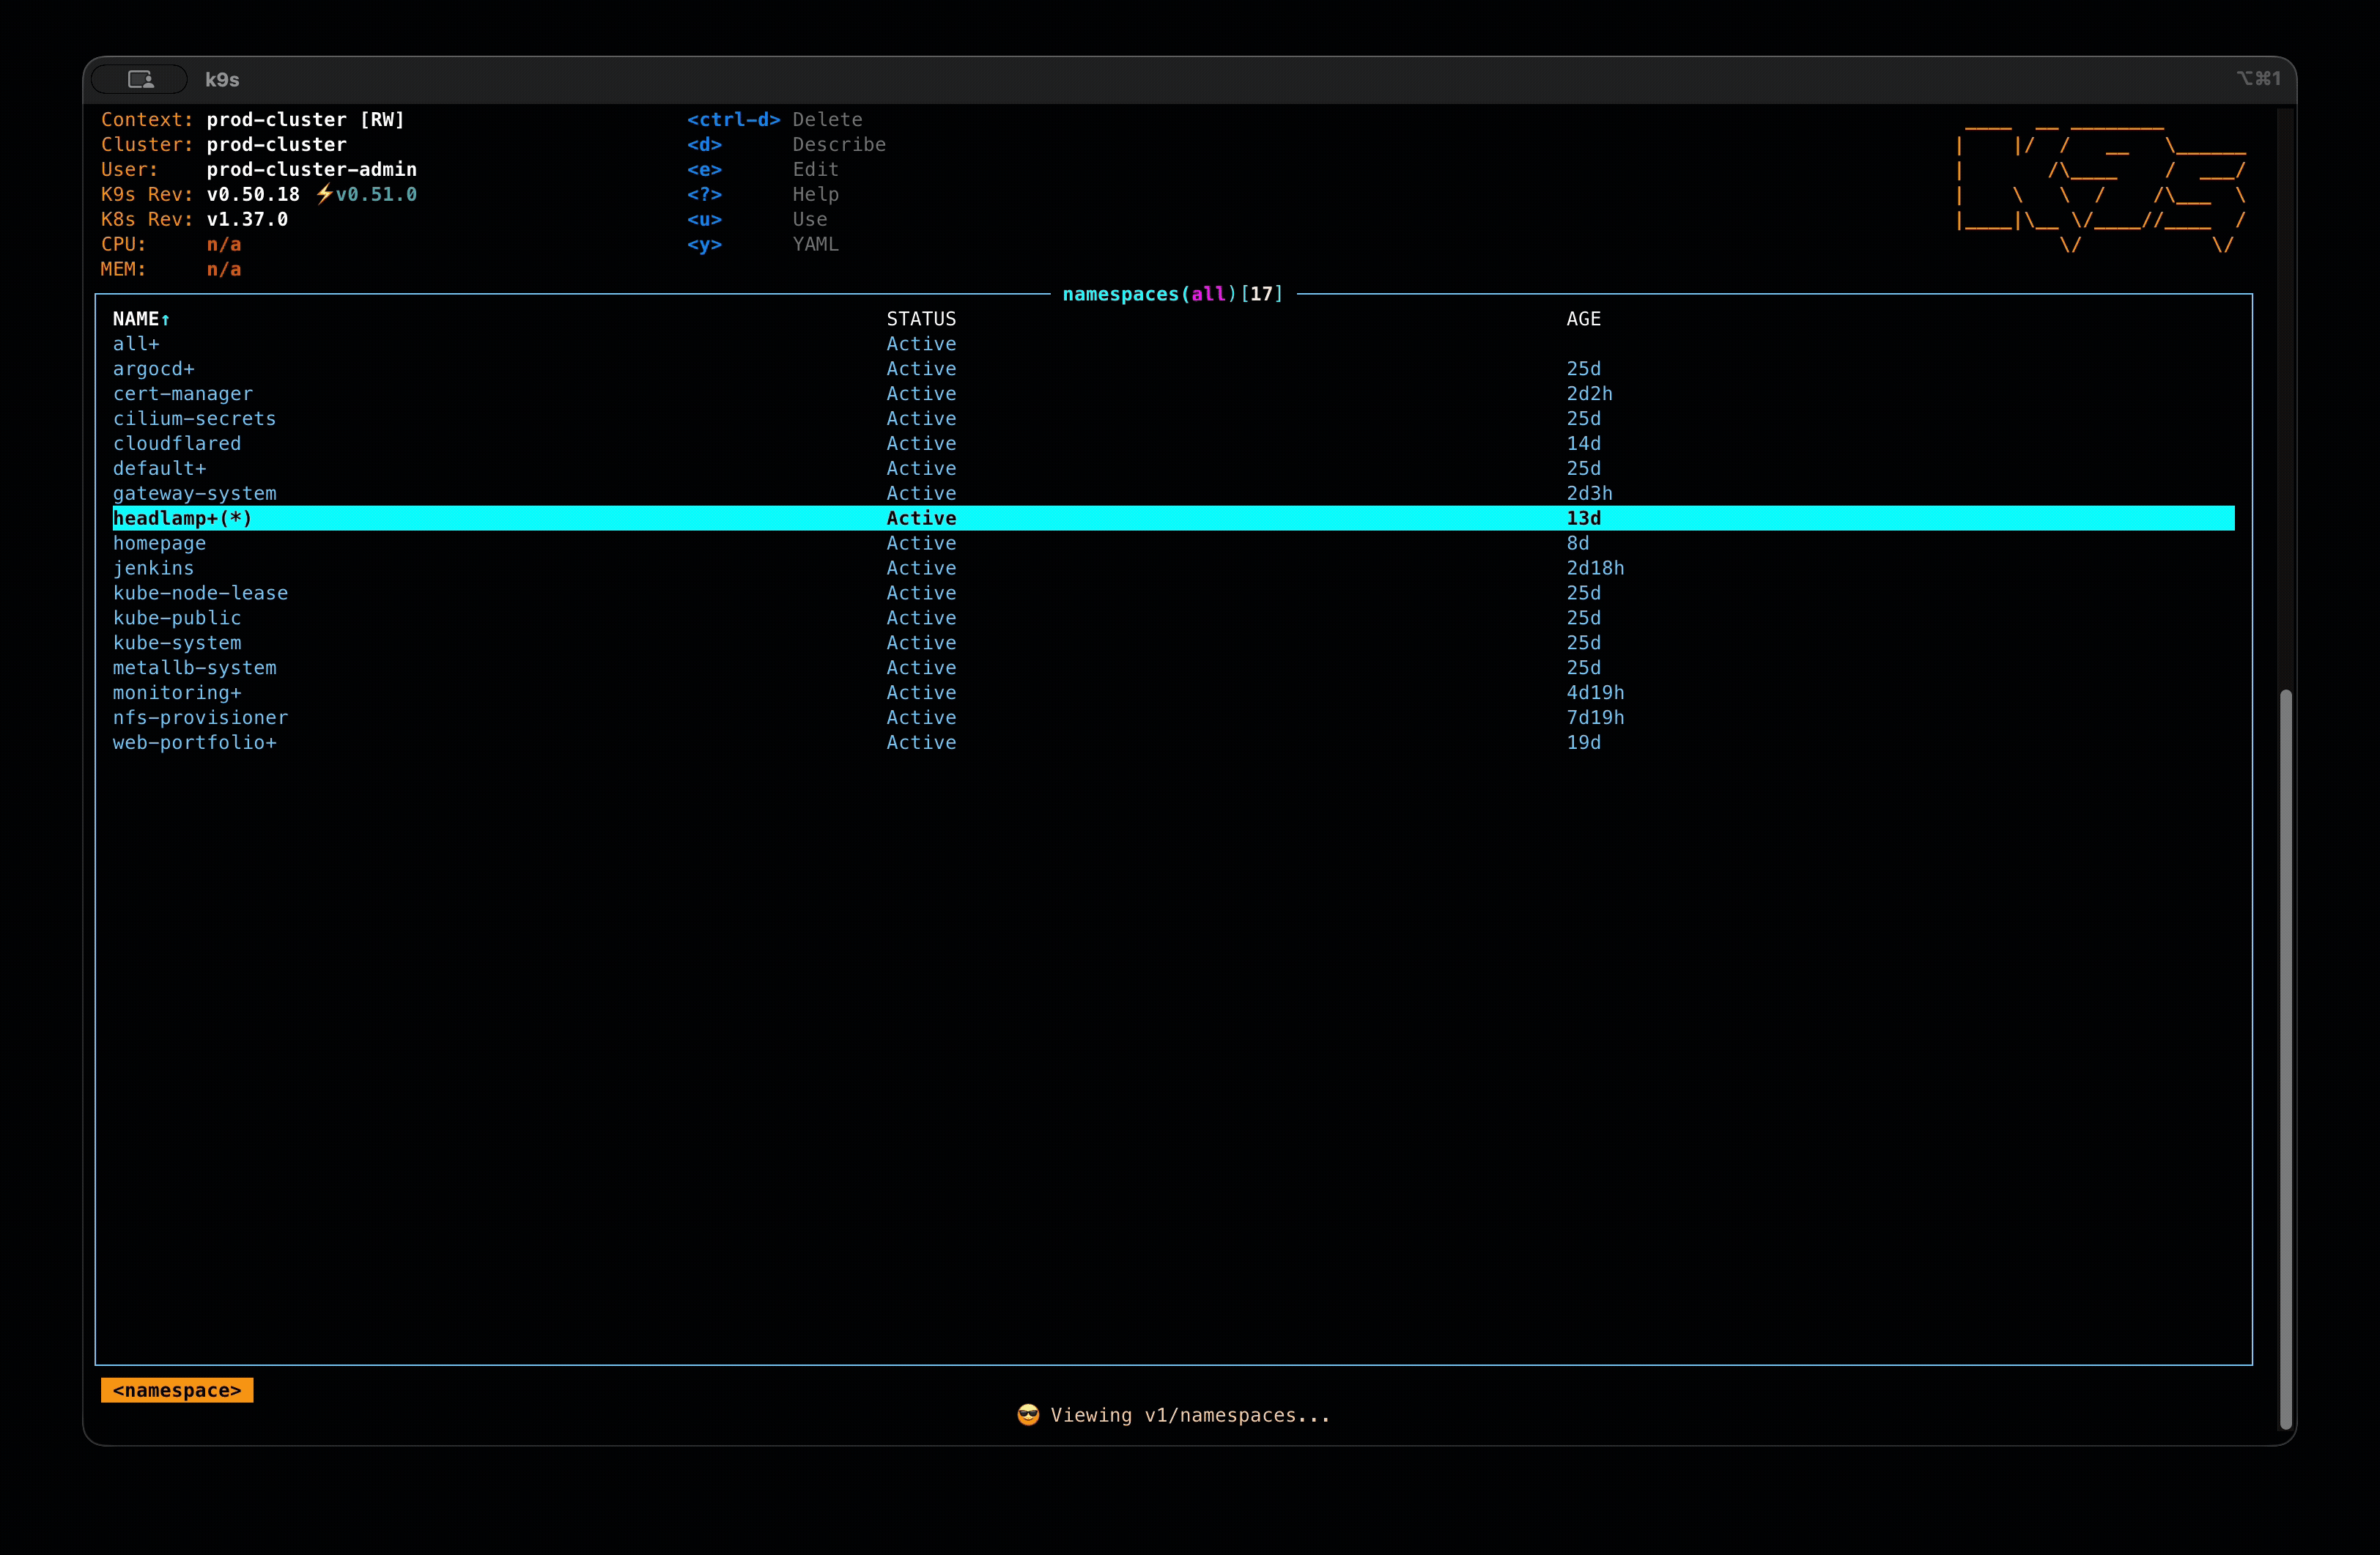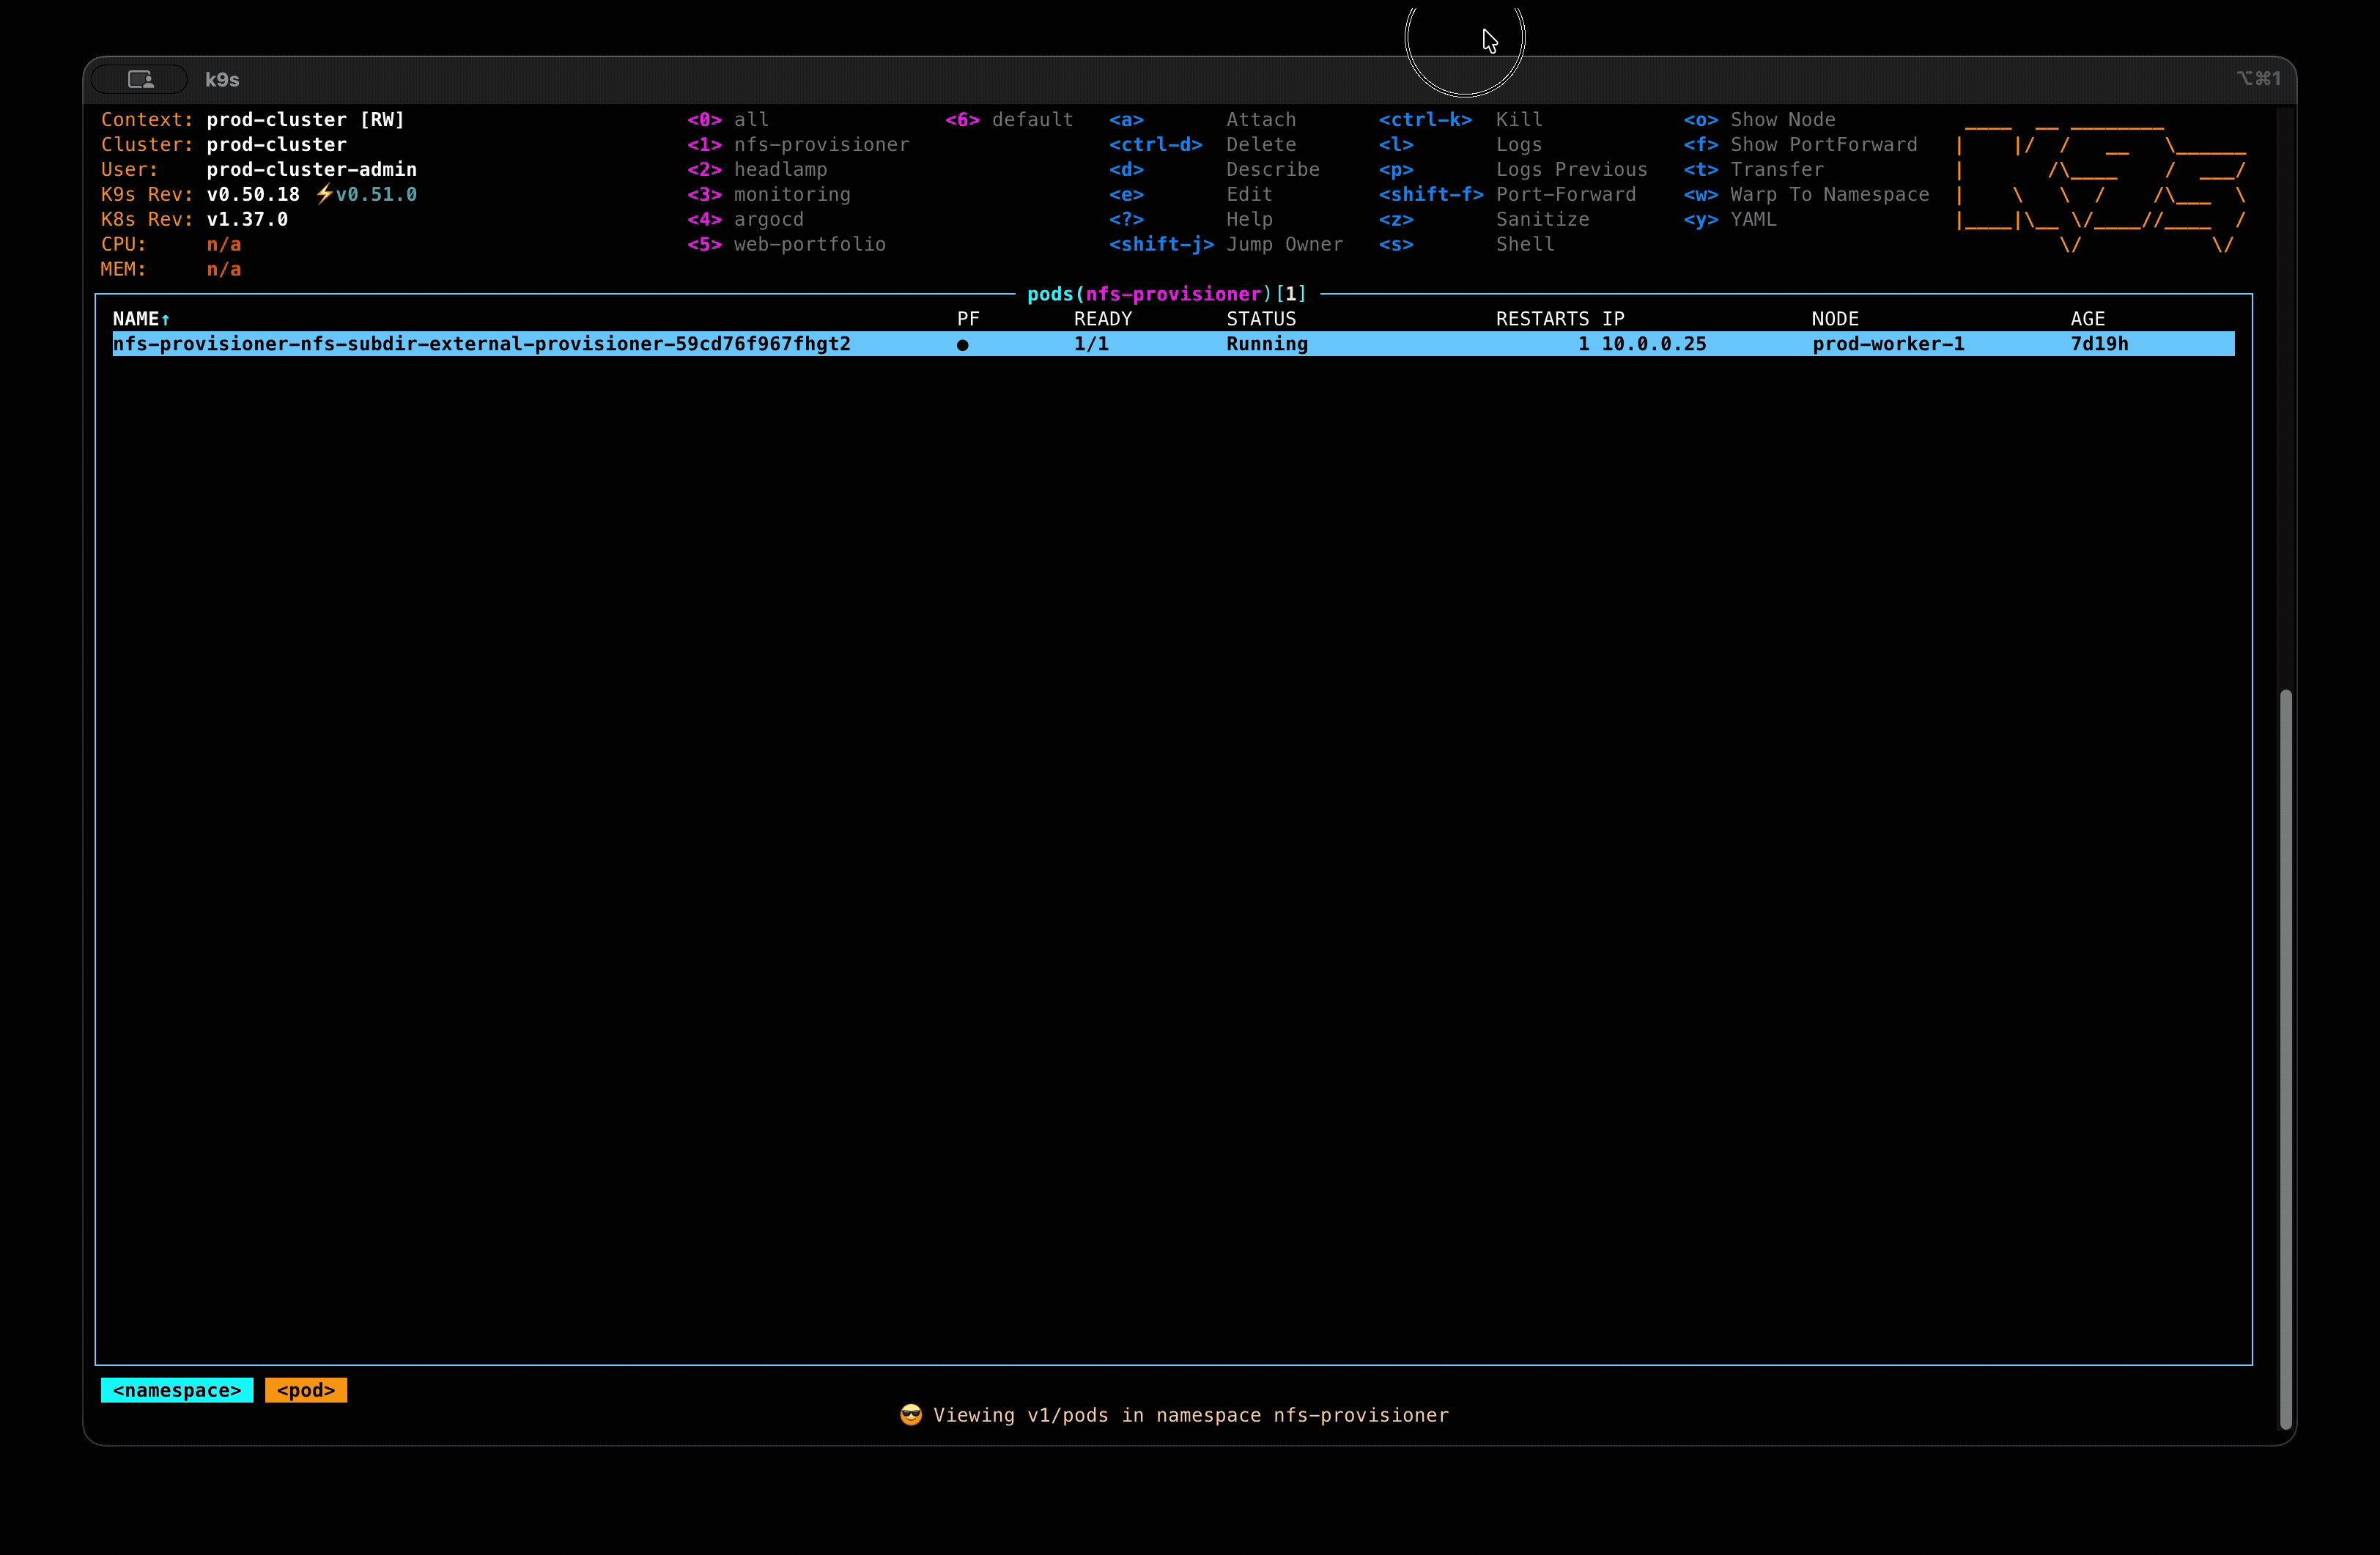
Homelab Platform concept artwork, full view
Kubernetes / Cilium / MetalLB / PrometheusConcept artwork
02

Self-directed / Automation

GitOps Delivery

Live Project
GitOps Delivery concept artwork, detail oneGitOps Delivery concept artwork, detail two
GitOps Delivery concept artwork, full view
ArgoCD / GitHub Actions / Trivy / GHCRConcept artwork
03

Urban Farming Partners / IoT

Connected Agriculture

View Experience
Connected Agriculture concept artwork, detail oneConnected Agriculture concept artwork, detail two
Connected Agriculture concept artwork, full view
Next.js / MQTT / Kafka / SwiftConcept artwork
01Homelab Platform

A continuously operated Kubernetes estate. Real workloads, real upgrades, real failure scenarios.

  • Two-tier homelab Kubernetes estate, continuously operated: a 3-node kubeadm cluster (Cilium CNI, MetalLB L2 load balancing, containerd) running production workloads, plus a K3s development cluster running Istio service mesh and Kyverno policy-as-code admission control ahead of promoting either to prod — both run through real upgrade, certificate-rotation, and failure scenarios
  • Hosts this portfolio and internal homelab services on the platform, with ingress and TLS termination, persistent storage classes, RBAC and namespace quotas, a private image registry, and a full Prometheus/Grafana + ELK observability stack — built to enterprise patterns
  • HA data tier: MariaDB Galera cluster behind an evaluated proxy layer (HAProxy / MaxScale / ProxySQL), with backup, restore, and node-loss drills
02GitOps Delivery

From commit to cluster. Infrastructure and applications reconciled from Git, with security built into delivery.

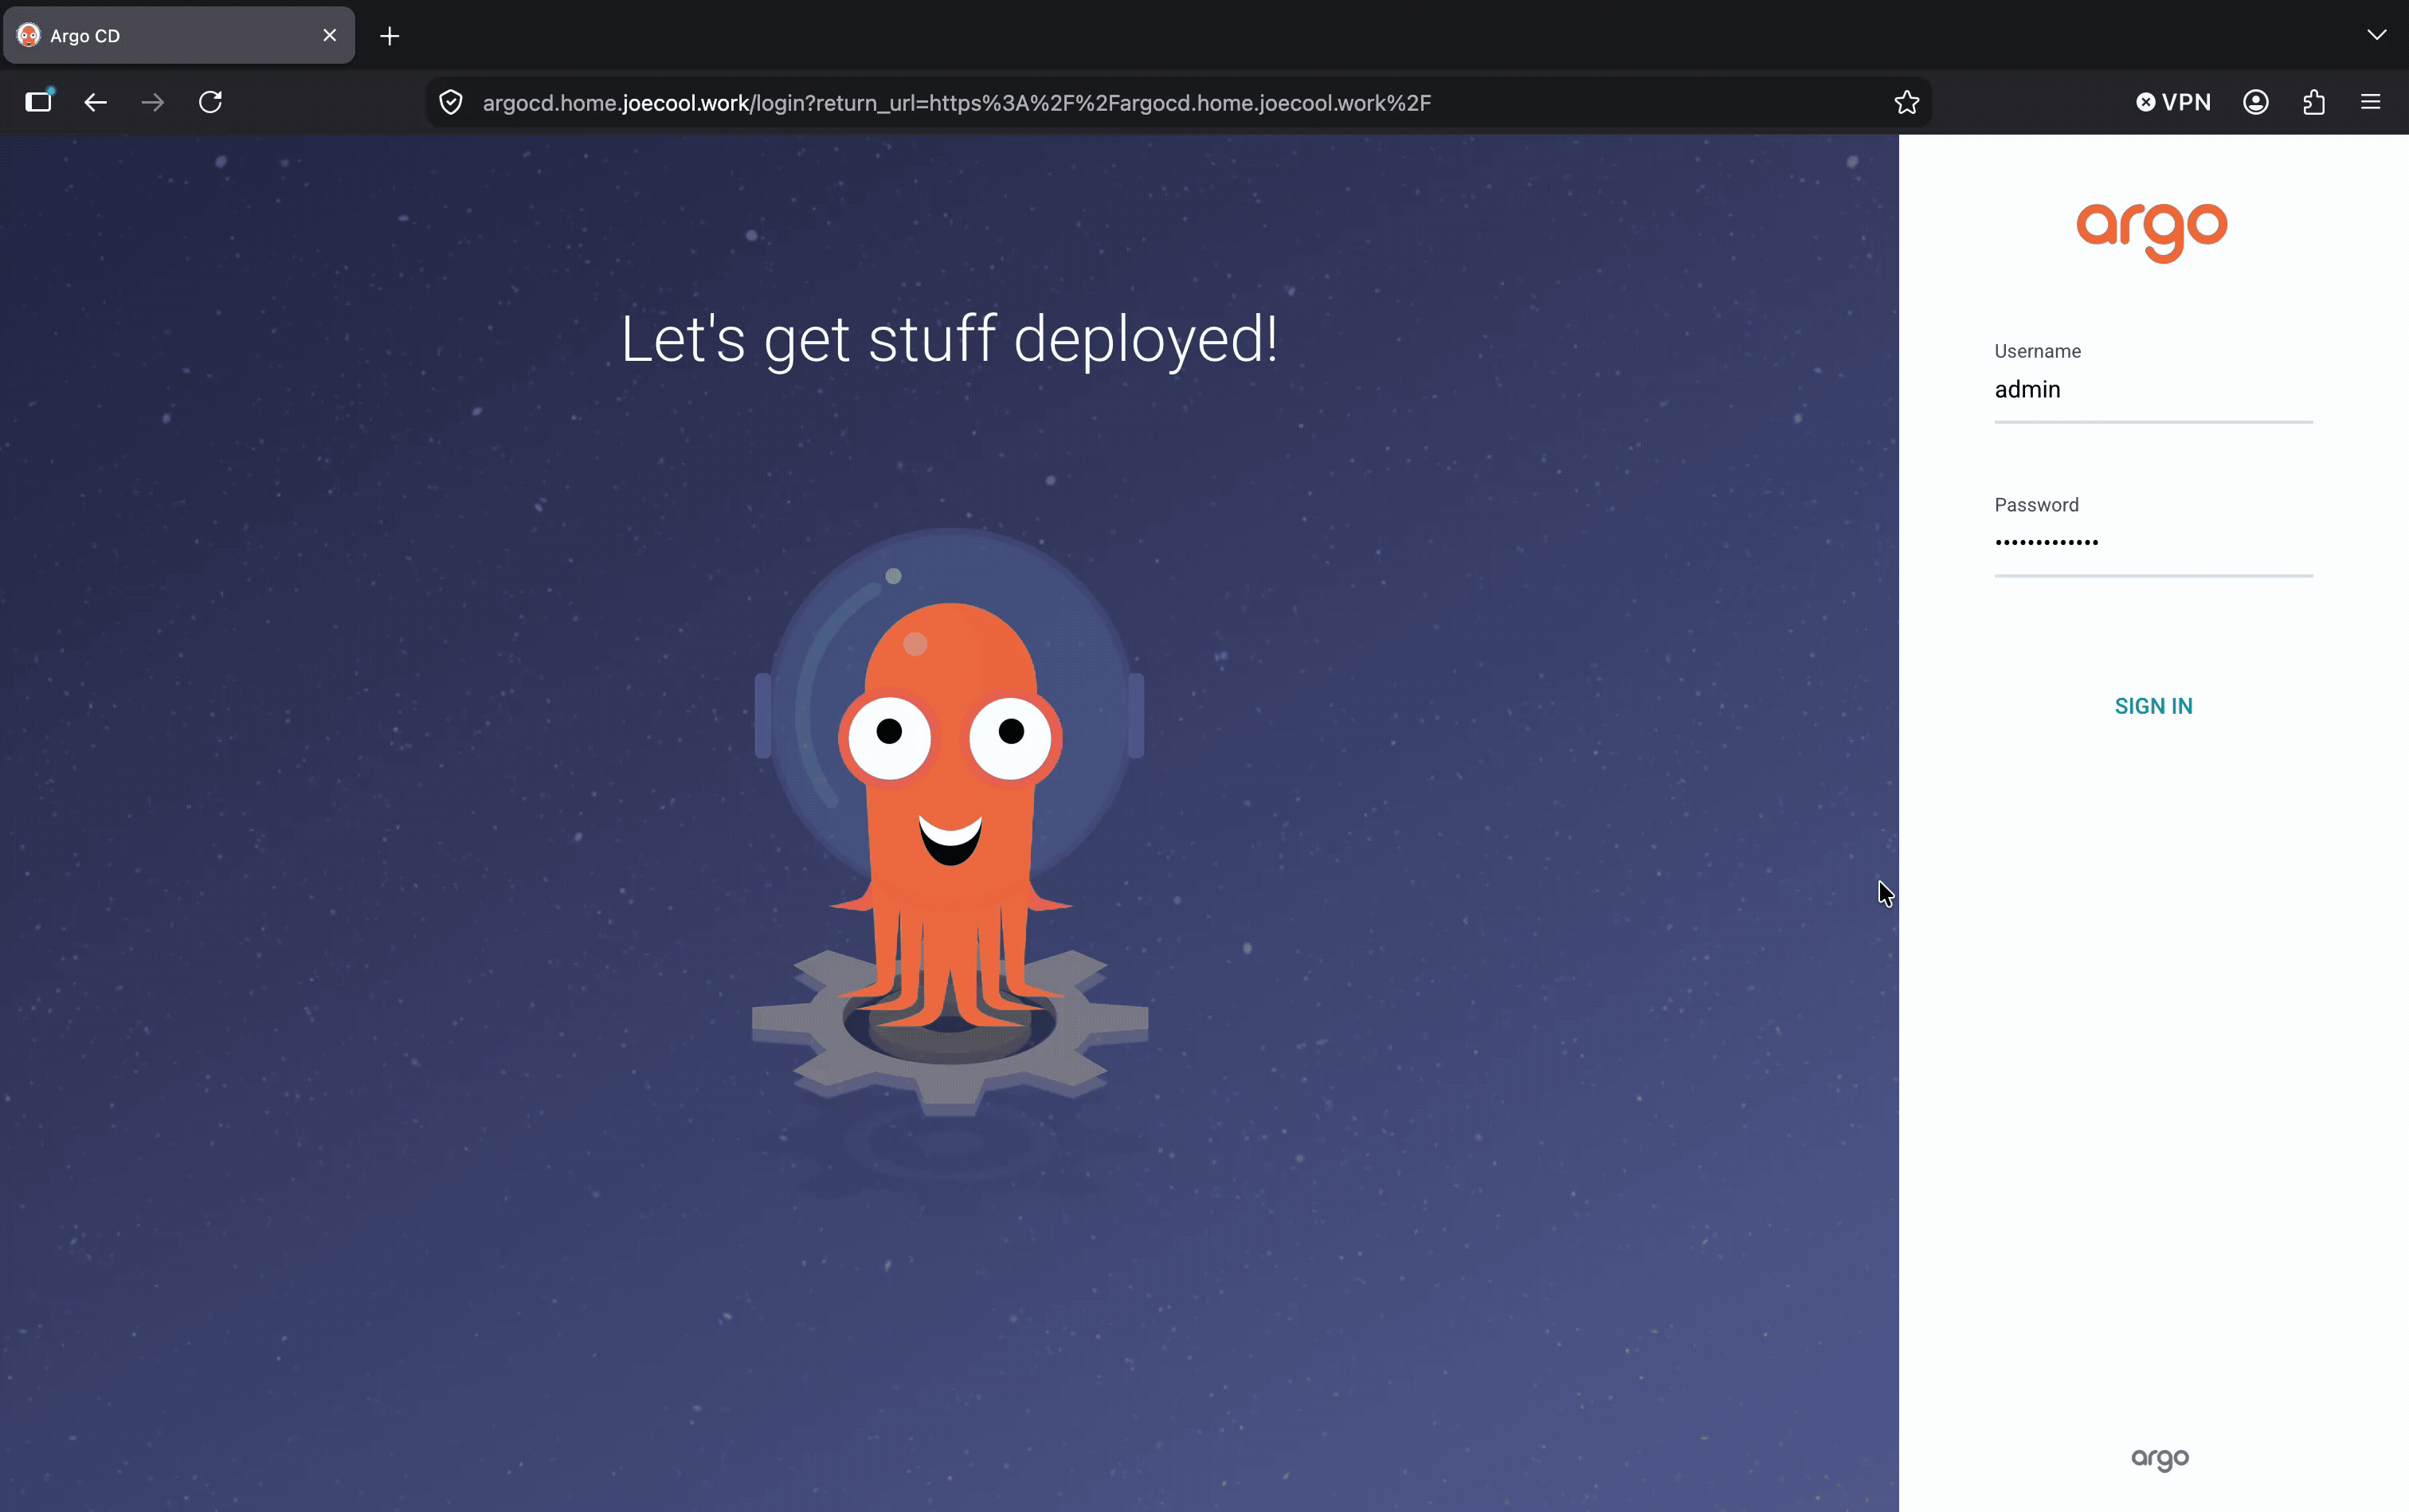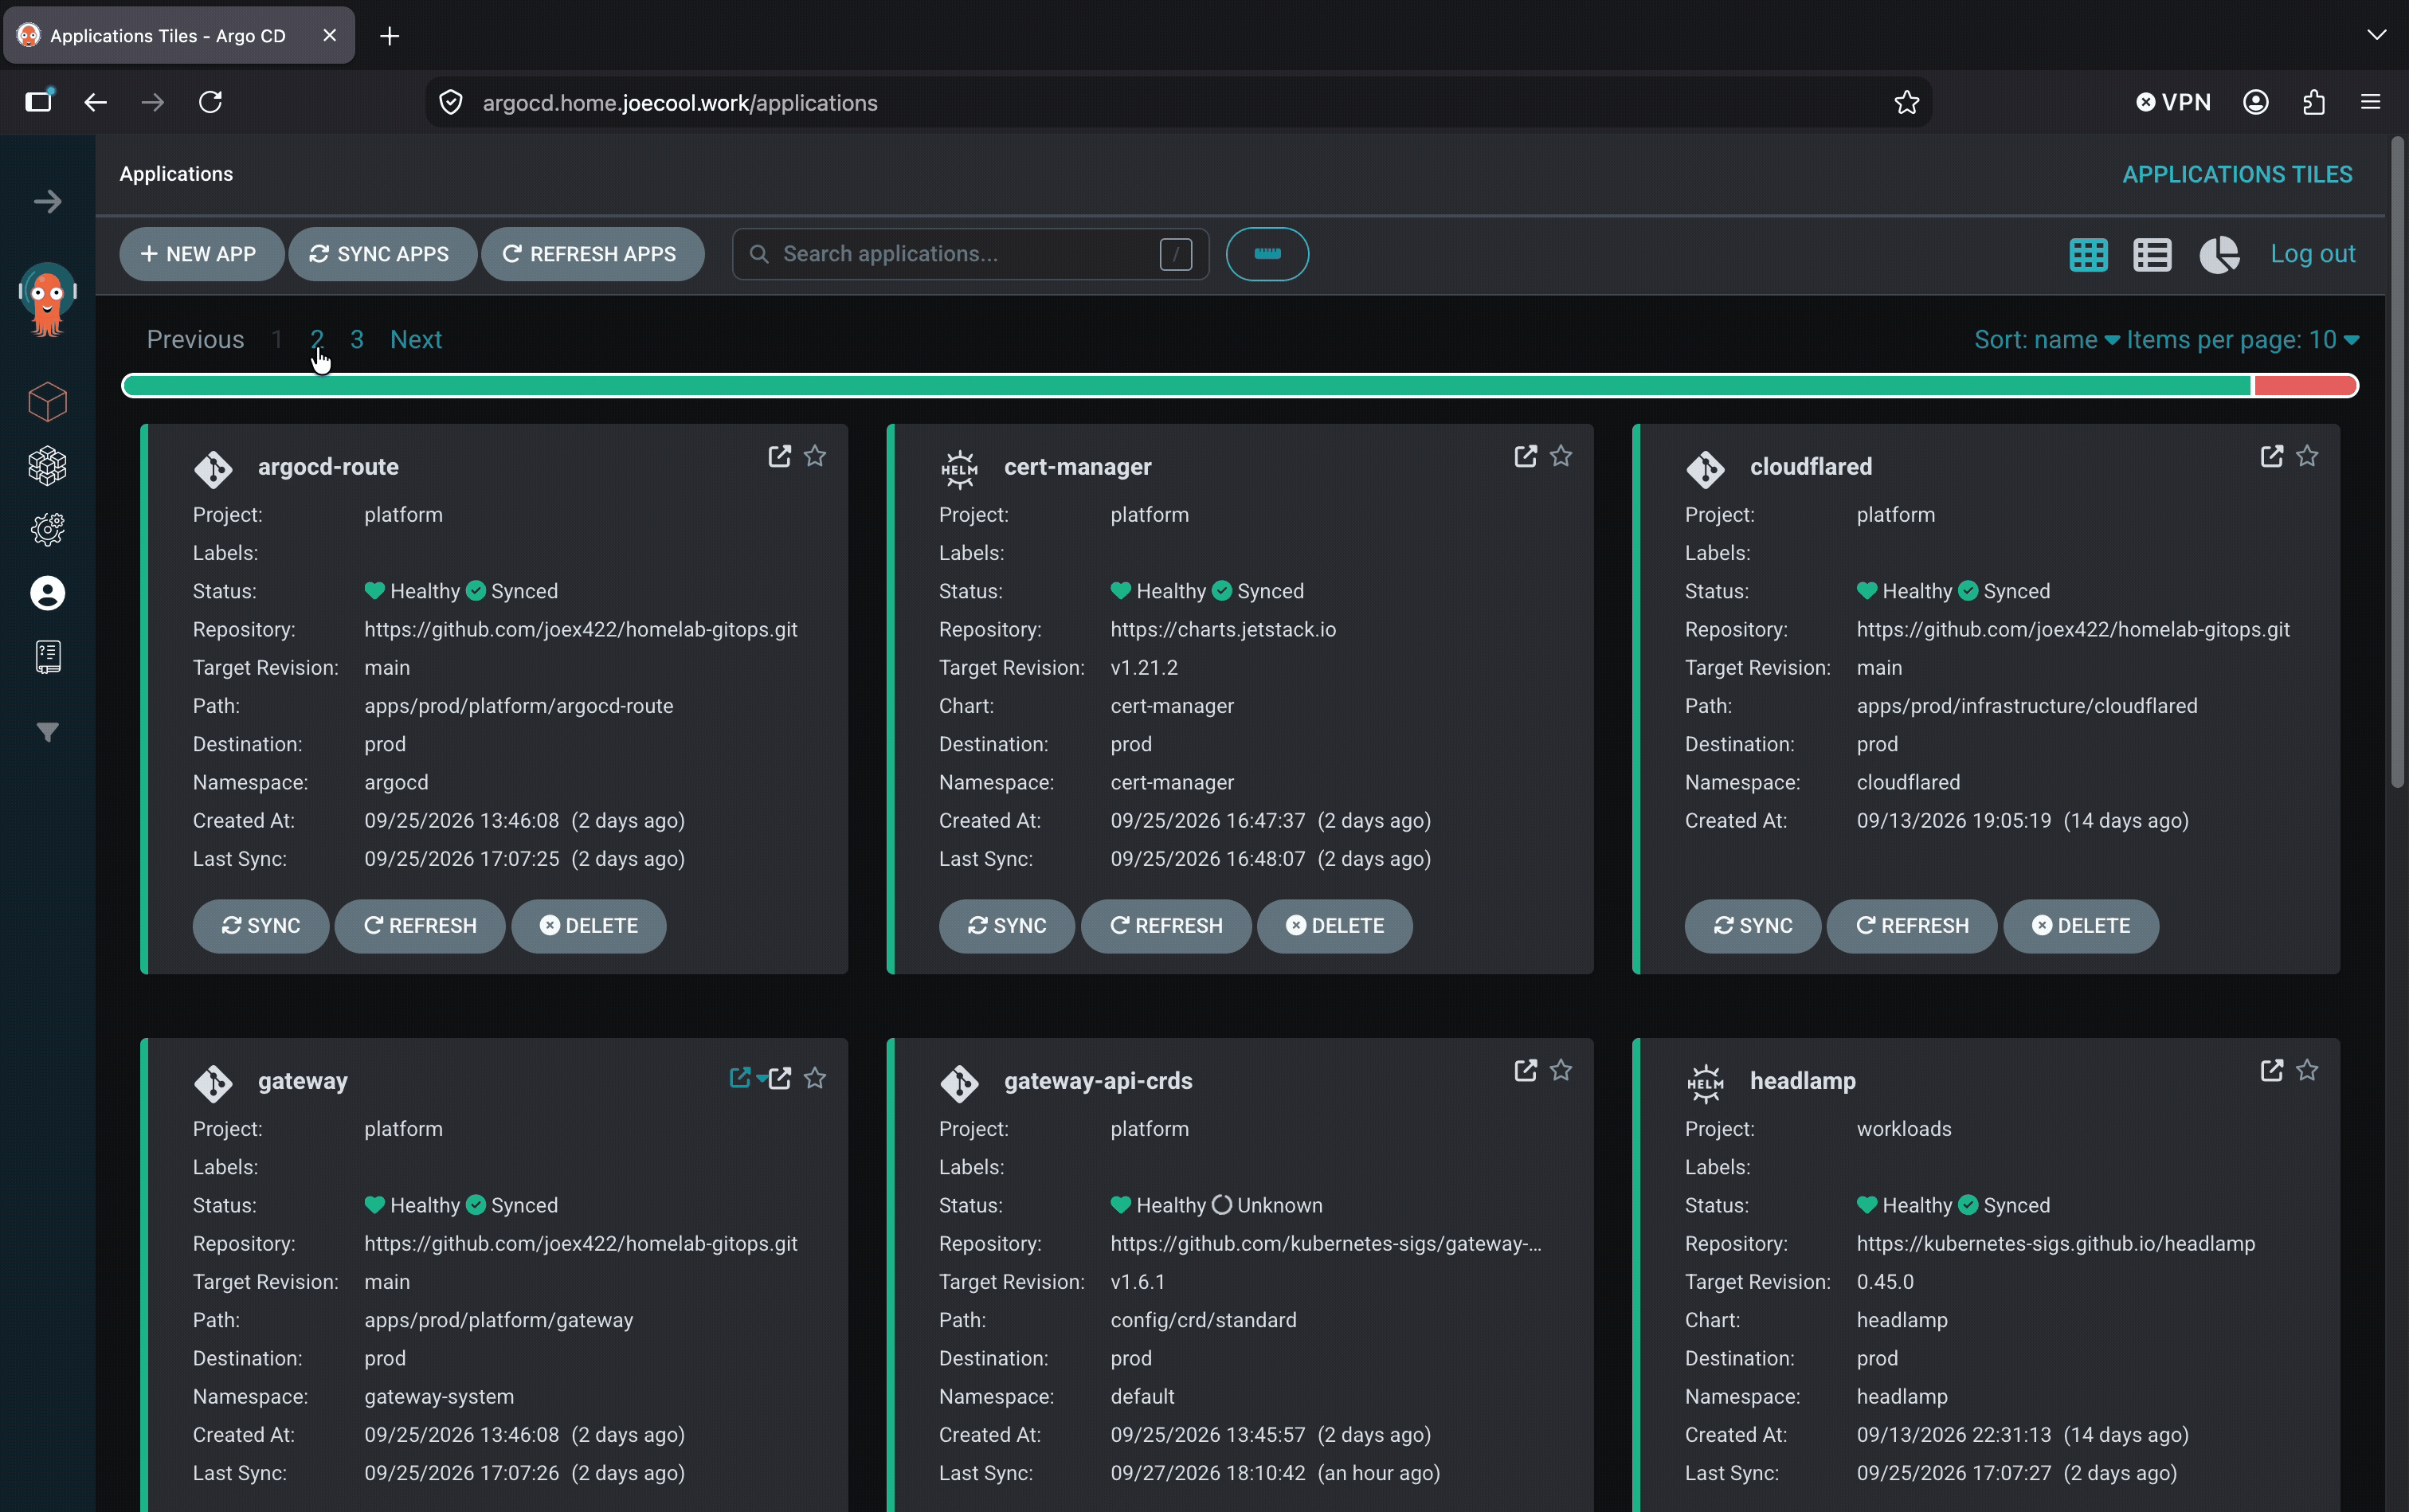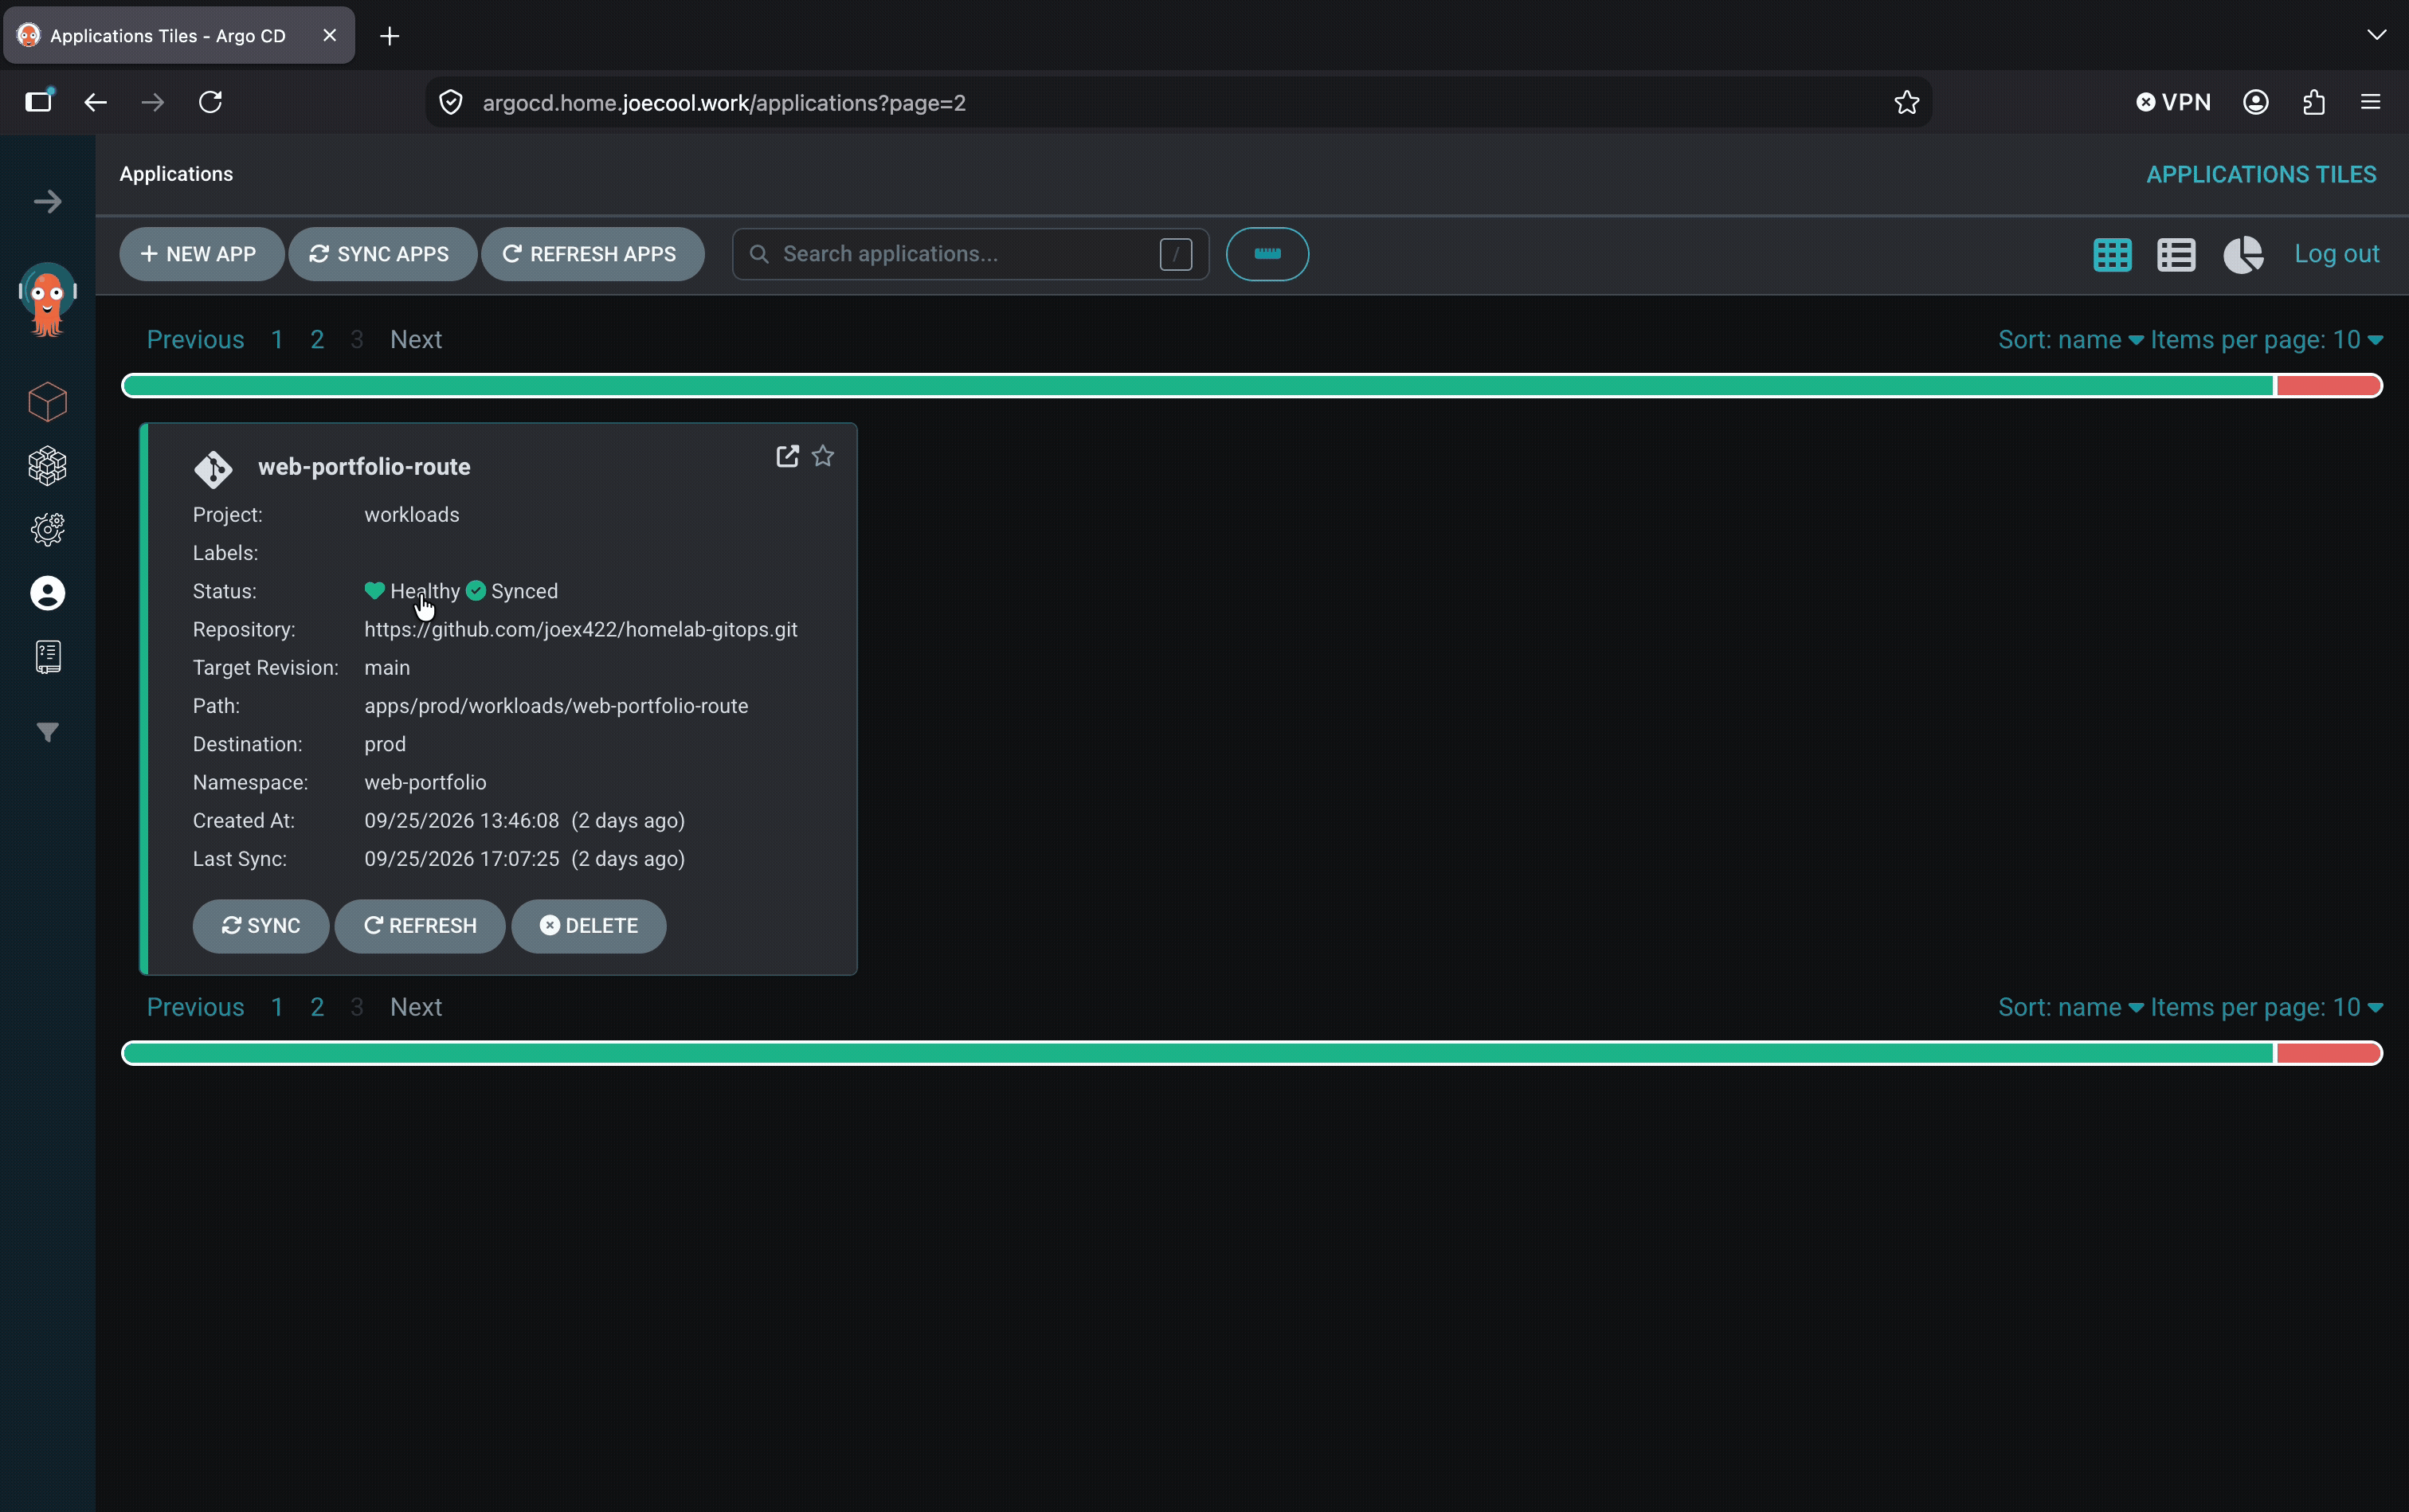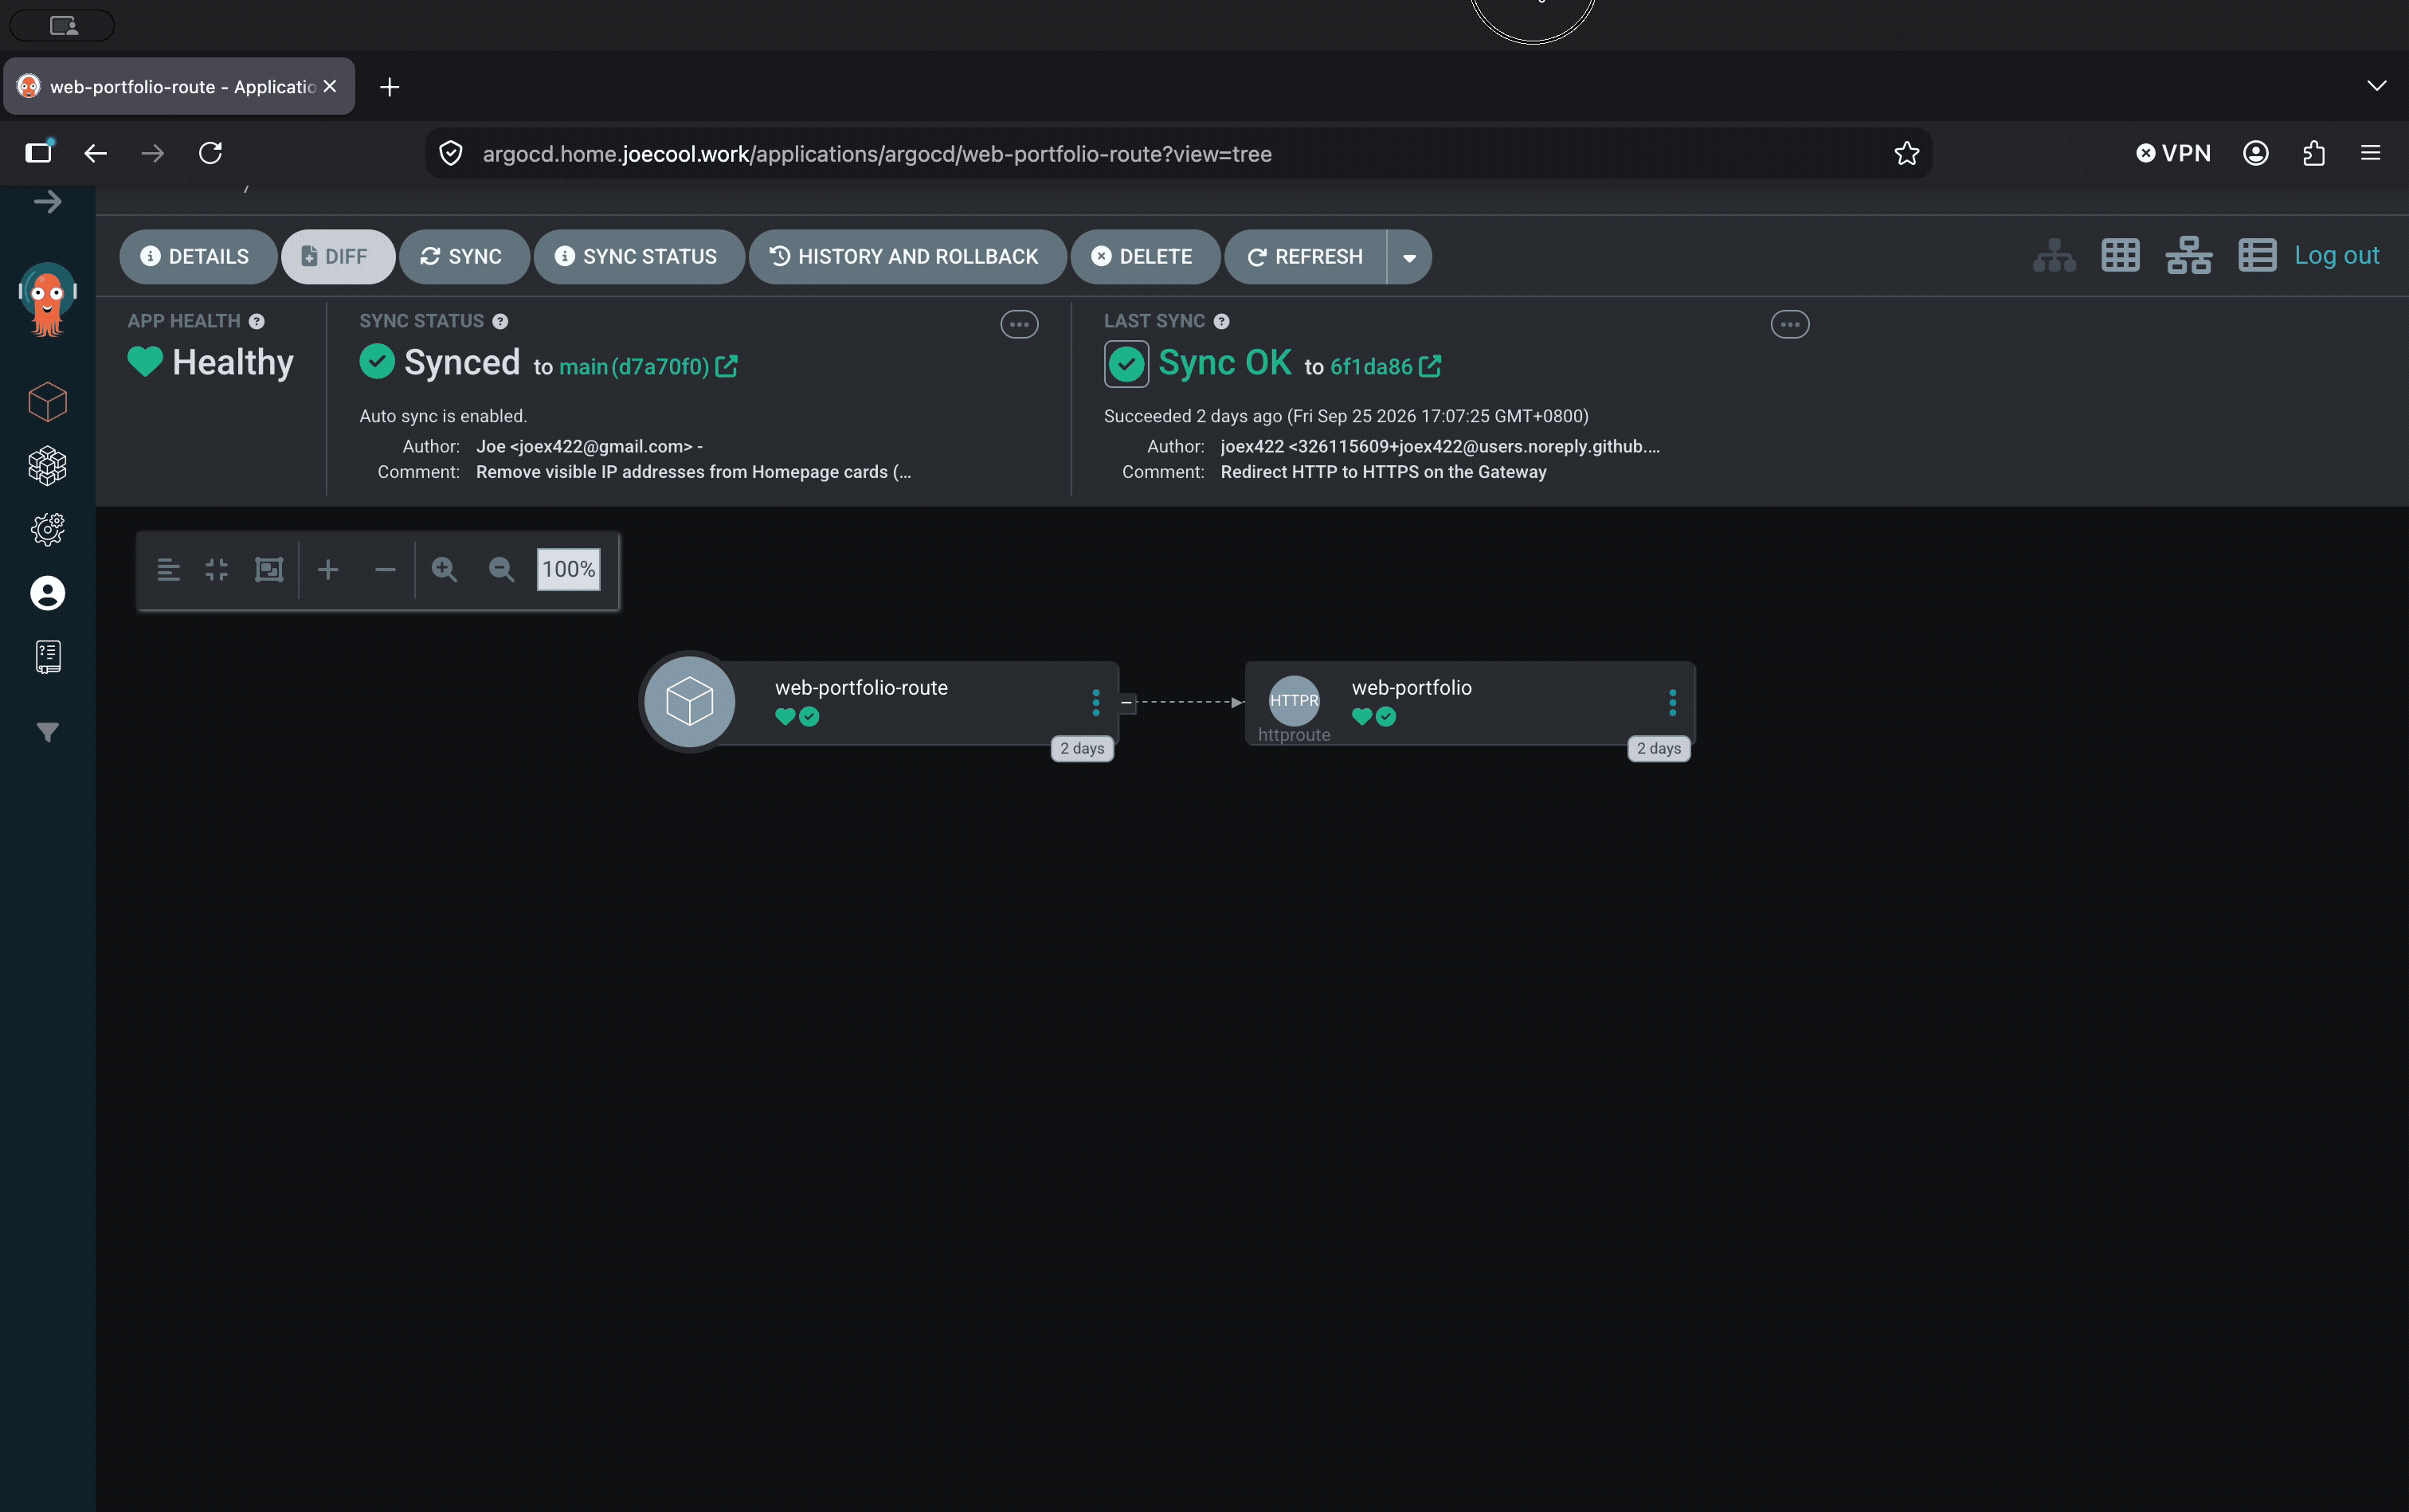
  • GitOps delivery with ArgoCD in an app-of-apps pattern — a root Application bootstraps every other workload from Git, with automated sync, pruning, and self-heal so cluster drift is reconciled rather than patched in place
  • CI/CD for this portfolio itself: GitHub Actions builds and publishes the container image to GHCR on every push to main, gated by a Trivy vulnerability scan of the image filesystem before it ships
  • Platform roadmap in progress: Gateway API for HTTP routing in place of classic ingress
03Connected Agriculture

An end-to-end sensor platform connecting real-time plant telemetry with dashboards, mobile apps, and analytics.
  • Delivered real-time dashboards for soil moisture, temperature, and humidity with MERN and Next.js.
  • Built MQTT and WebSocket ingestion into Confluent Kafka, with query-ready datasets for analysts.
  • Created native iPadOS and Flutter companion apps, secured REST APIs with JWT, and automated delivery with Docker and GitHub Actions.

Experience

From software to systems
NCS

AI Platform Engineer

NCS · Nov 2025 — Present

Video intelligence and enterprise AI infrastructure — on-prem, government security baseline.
OpenShiftGPU-backed nodesMariaDB GaleraHAProxyELKTerraformVaultCyberArkEntra IDRHEL
  • Operate the OpenShift estate — namespaces, RBAC and SCC policy, network policies, quotas, Routes, HAProxy ingress, PV/PVC storage
  • Built and run MariaDB Galera multi-master HA — survives node loss with no failover downtime, fronted by HAProxy for routing and health checks
  • ELK monitoring across cluster, systemd, and MariaDB logs — dashboards and alerts that surface failures before users report them
  • Own the Linux layer — patching, kernel and package management, resource limits, storage mounts, sequenced to keep production up
  • Day-1 build and Day-2 ops on an enterprise AI platform running on GPU-backed nodes, plus database ownership of schema, tuning, backup and recovery
  • Provision infrastructure with Terraform — environments rebuilt from code, not reassembled by hand
  • Harden to CIS and government IM8 baselines; remediate scan findings and produce the audit evidence
  • Privileged access through CyberArk, service credentials in Vault — no long-lived secrets in configs or node images
  • Identity governance across Entra ID and on-prem LDAP — user/group lifecycle, RBAC, Azure Policy — over a mixed Linux and Windows estate
  • IPSec VPN tunnels so field devices reach internal systems without public exposure
Singtel

DevOps / Infrastructure Engineer

Singtel · Aug 2024 — Sep 2025

Infrastructure and delivery behind Singtel's NaaS, 5G, and multi-access edge computing products.
KubernetesHelmArgoCDJenkinsZabbixTerraformAnsiblePythonOpenSearch
  • First responder across Linux servers and Kubernetes clusters — traced failures node to pod to service, with root-cause analysis feeding back into runbooks
  • Administered Kubernetes clusters for edge workloads — node management, workload placement, resource limits, Helm-packaged deployments
  • Full-stack Zabbix monitoring across infrastructure, network, and application metrics
  • Jenkins CI/CD pipelines and ArgoCD rollouts — Git as source of truth, cluster drift reconciled automatically instead of patched in place
  • Troubleshot and performance-tuned OpenSearch, MySQL, Redis, MongoDB, and container workloads
  • Owned OS patching across the Linux fleet — systems current, vulnerabilities closed, no production downtime
  • Terraform for provisioning; Ansible for daily Docker and virtualised operations
  • Python automation for security (IoC IP filtering) and operations (system health checks)
Urban Farming Partners Singapore

Software Engineer

Urban Farming Partners Singapore · Oct 2022 — Apr 2024

End-to-end IoT monitoring platform turning plant-sensor telemetry into dashboards, mobile apps, and analyst-ready datasets.
MERNNext.jsVercelMQTTWebSocketsConfluent KafkaSwiftFlutterJWTDockerGitHub Actions
  • Designed and delivered an end-to-end IoT monitoring platform, turning raw sensor data from plant-monitoring microcontrollers into real-time dashboards, mobile apps, and analyst-ready datasets
  • Built responsive dashboards with the MERN stack and Next.js, deployed on Vercel, visualising soil moisture, temperature, and humidity readings
  • Built MQTT and WebSocket ingestion feeding a Confluent Kafka streaming layer, cleaning, transforming, and aggregating telemetry from a fleet of plant-monitoring devices
  • Partnered with data analysts to define schemas and expose query-ready datasets for trend analysis and anomaly detection
  • Delivered a native iPadOS app in Swift for on-site monitoring and alerts, plus a cross-platform Flutter companion app
  • Secured REST APIs with JWT authentication and role-based access control
  • Implemented CI/CD with Docker and GitHub Actions, plus monitoring for pipeline health and device uptime

The toolkit

KubernetesOpenShiftDockerHelmTerraformAnsibleJenkinsGitLabArgoCDGitPythonBashJavaPrometheusGrafanaElasticsearchKibanaLogstashOpenSearchZabbixMariaDBMySQLMongoDBRedisHashiCorp VaultAWSAzureRHELCentOSRocky LinuxUbuntuWindows Server
Kubernetes & Containers

Kubernetes (CKA) · node lifecycle · etcd health · RBAC · network policies · resource quotas · PV/PVC & storage classes · OpenShift (OCP 4.x) · Routes · SCCs · HAProxy ingress · private registry & image mirroring · K3s · Istio · Helm · Docker

Reliability & Observability

Incident response · root-cause analysis · runbooks · ELK / Elasticsearch / Logstash / Kibana · OpenSearch · Prometheus · Grafana · Zabbix · log aggregation · alerting · capacity & performance monitoring

High Availability

MariaDB Galera (multi-master HA) · HAProxy proxy tier · backup & recovery · JVM/Java tuning (heap, Metaspace, GC flags) · container memory budgeting

Linux Platform

RHEL / CentOS / Rocky · Ubuntu administration · OS patching & kernel upgrades · reboot sequencing · dnf/yum · systemd · SELinux · firewalld · auditd · ulimits/cgroups · NFS & iSCSI/SMB storage mounts · LVM · Windows Server

Automation & IaC

Terraform · Ansible · Jenkins · GitLab CI · ArgoCD / GitOps · Git · Python · Bash · operational runbooks

Security & Hardening

CIS benchmark hardening · IM8-aligned controls · CVE triage · SSH cipher/MAC hardening · HashiCorp Vault · CyberArk PAM · LDAP · Azure AD (Entra ID) IAM & RBAC · secrets management · IPSec VPN · DevSecOps · Kyverno policy-as-code · Trivy vulnerability scanning

Data & Cloud

MySQL · MongoDB · Redis · AWS (EC2, S3, IAM, CloudWatch, VPC) · Azure (Entra ID, RBAC, Policy) · hybrid & on-prem integration · Proxmox virtualisation
Certified & verified

Certified Kubernetes Administrator logo

Certified Kubernetes Administrator (CKA)

Cloud Native Computing Foundation · Aug 2026

View certificate

Education

BSc Computing Science (Honours)

Singapore Institute of Technology

Aug 2022 — Apr 2025

Diploma in Business Process with Systems Engineering

Temasek Polytechnic

Apr 2017 — Feb 2020

More from the homelab
  • Two-tier homelab Kubernetes estate, continuously operated: a 3-node kubeadm cluster (Cilium CNI, MetalLB L2 load balancing, containerd) running production workloads, plus a K3s development cluster running Istio service mesh and Kyverno policy-as-code admission control ahead of promoting either to prod — both run through real upgrade, certificate-rotation, and failure scenarios
  • GitOps delivery with ArgoCD in an app-of-apps pattern — a root Application bootstraps every other workload from Git, with automated sync, pruning, and self-heal so cluster drift is reconciled rather than patched in place
  • Hosts this portfolio and internal homelab services on the platform, with ingress and TLS termination, persistent storage classes, RBAC and namespace quotas, a private image registry, and a full Prometheus/Grafana + ELK observability stack — built to enterprise patterns
  • CI/CD for this portfolio itself: GitHub Actions builds and publishes the container image to GHCR on every push to main, gated by a Trivy vulnerability scan of the image filesystem before it ships
  • HA data tier: MariaDB Galera cluster behind an evaluated proxy layer (HAProxy / MaxScale / ProxySQL), with backup, restore, and node-loss drills
  • Platform roadmap in progress: Gateway API for HTTP routing in place of classic ingress
  • Bash-based CKA exam simulator running against a disposable k3d sandbox; AWS serverless projects for SAA preparation